SecuLayer, in collaboration with SK Shieldus, is demonstrating the KISA supply chain security model... "Leading AI-Native supply chain security by expanding into AIBOM and XBOM"
- Presenting the 'AI-Native Supply Chain Security' paradigm and accelerating the roadmap for AIBOM and XBOM expansion
- Implementation of an integrated model combining SecuLayer's intelligent vulnerability analysis platform with SK Shieldus's real-world monitoring capabilities
- Sharing the results and achievements of the virtuous cycle supply chain security system at the 'IITP Tech & Future Insight Concert 2026'
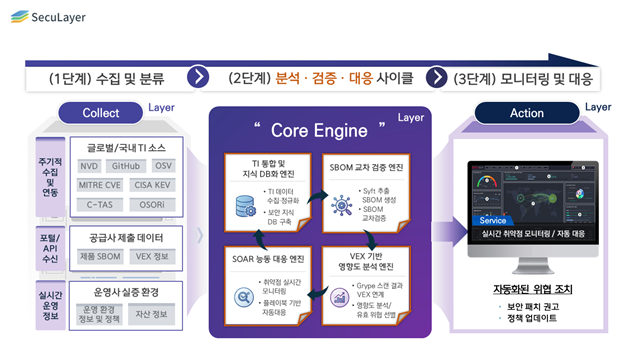
SecuLayer's roadmap for integrated management and automated response to supply chain threats based on SBOM – provided by SecuLayer
SecuLayer (CEO Lee Jae-woo), a specialized company in AI-based information security solutions, announced that it is accelerating the establishment of a software (SW) supply chain security management system in consortium with SK Shieldus as the leading organization of the '2026 SW Supply Chain Security Model Establishment Support Project' organized by the Ministry of Science and ICT and the Korea Internet & Security Agency (KISA).
With the recent widespread adoption of open-source and commercial SW packages, the threats targeting the entire process of software development and distribution have rapidly increased. In response, major countries globally, including the U.S. Executive Order (EO 14028) and the European Cyber Resilience Act (CRA), are swiftly institutionalizing the mandatory management of software components through the 'Software Bill of Materials (SBOM)' to systematically identify and manage potential vulnerabilities. The introduction of a systematic security model to ensure compliance with global regulations and supply chain resilience is urgently needed in domestic public and corporate environments.
Based on KISA's SW supply chain security guidelines and specialized technical support, this project aims to implement an 'Intelligent SBOM Integrated Management and Automated Response System for Supply Chain Threats'. The core is to automate the entire pipeline from the systematic management of the software component list through SBOM generation to vulnerability detection, risk assessment, automated response, and post-verification, integrating the potential threats of the software supply chain on a single platform.
In the execution of the project, SecuLayer will lead the development of AI-based SBOM analysis engine and vulnerability automated response platform technology, while SK Shieldus, equipped with the largest cybersecurity operational capabilities in Korea, will focus on validating effectiveness in real monitoring infrastructure and operational environments and optimizing the operational model. Currently, both companies are implementing SBOM and vulnerability correlation analysis, dynamic risk visibility, threat response, and automated reporting systems, and conducting multifaceted validation assessments linked to real operational environments.
In particular, this platform proactively integrates the standard for exchanging vulnerability exploitability information, VEX (Vulnerability Exploitability eXchange). By precisely filtering whether vulnerabilities identified through SBOM can be executed and exploited in actual service environments (Exploitable), it significantly reduces false positives that cause fatigue for security managers and allows for a focused allocation of security resources to high-risk vulnerabilities that require immediate response.
Furthermore, the SBOM and VEX data from the development and supply stages are smoothly transmitted to the operational stage, and the threats identified and mitigation results at the operational and monitoring stages are fed back to the entire development and supply chain, completing a 'bidirectional virtuous cycle security governance'. Even when new open-source vulnerabilities emerge, the structure allows for real-time tracking of vulnerable assets, verification of actual impact in the operational environment, and immediate application of response measures, continuously improving the security of the entire supply chain.
Moreover, SecuLayer plans to leverage this demonstration project as a stepping stone to expand into an 'AI Bill of Materials (AIBOM)' that manages the components and training data of AI models, and an extended bill of materials (XBOM) that broadens the management scope beyond software to include data and hardware, actively promoting the 'AI-Native Supply Chain Security' strategy.
SecuLayer participated in the 'IT Mega Vision X IITP Tech & Future Insight Concert 2026' held on September 16, co-hosted by the Information and Communication Planning and Evaluation Institute (IITP) and the Electronic Times, operating an exhibition booth to introduce the progress of this project and the SBOM-based technology roadmap to industry stakeholders and share next-generation supply chain security strategies.
SecuLayer emphasized, “To effectively manage the vast vulnerabilities identified through SBOM, it is essential to link with VEX (Vulnerability Exploitability information), which can assess the impact and exploitability in actual operational environments.” It explained that it is crucial to go beyond merely identifying the existence of vulnerabilities to selecting risks that require actual response and prioritizing actions.
It further revealed plans to expand the scope of security management from existing software to AIBOM (AI Bill of Materials), which enhances the transparency of AI models and components, and ultimately to XBOM, which encompasses the configuration information of software, data, and hardware. Through this, it aims to establish 'AI-Native Supply Chain Security', considering security elements across the entire supply chain from the design stage with AI as the core foundation of security.
The consortium plans to complete simulated penetration training and threat response scenario validation based on the real platform within the year and distribute a supply chain security reference model.
SecuLayer CEO Lee Jae-woo stated, "This KISA demonstration project is significant in that it presents an effective supply chain security solution by combining SecuLayer's advanced AI data analysis technology with SK Shieldus's extensive real-world monitoring and operational know-how." He emphasized, “This construction model, combining the monitoring and analysis capabilities of SecuLayer and SK Shieldus, will establish itself as a model case that can be expanded across the public, private, and security ecosystems, leading to a true standard of 'AI-Native Supply Chain Security' that expands into AIBOM and XBOM.”
Related News

[ISEC 2026 On-Site Sketch] A New Partnership Between AI and Humans! The Future of Next-Generation Security Monitoring and Supply Chain (SBOM) Security Presented by SecuLayer
Hello, this is SecuLayer. SecuLayer successfully participated in the ‘ISEC 2026 (20th International Security Conference)…
K-Security Alliance Formed Between Leading Domestic Companies SecuLayer and QuadMiner, Strategic Business Agreement Signed
-Proposing an AI-based 'Complete Security Defense System' through context data-driven security observability and integra…

[Event Sketch] SecuLayer Introduces the eGISEC 2026 Participation Site!
[Event Sketch] eGISEC 2026 (15th Electronic Government Information Security Solution Fair) Hello, this is SecuLayer. Sec…